📉 Bearish
⏱ 3 min read
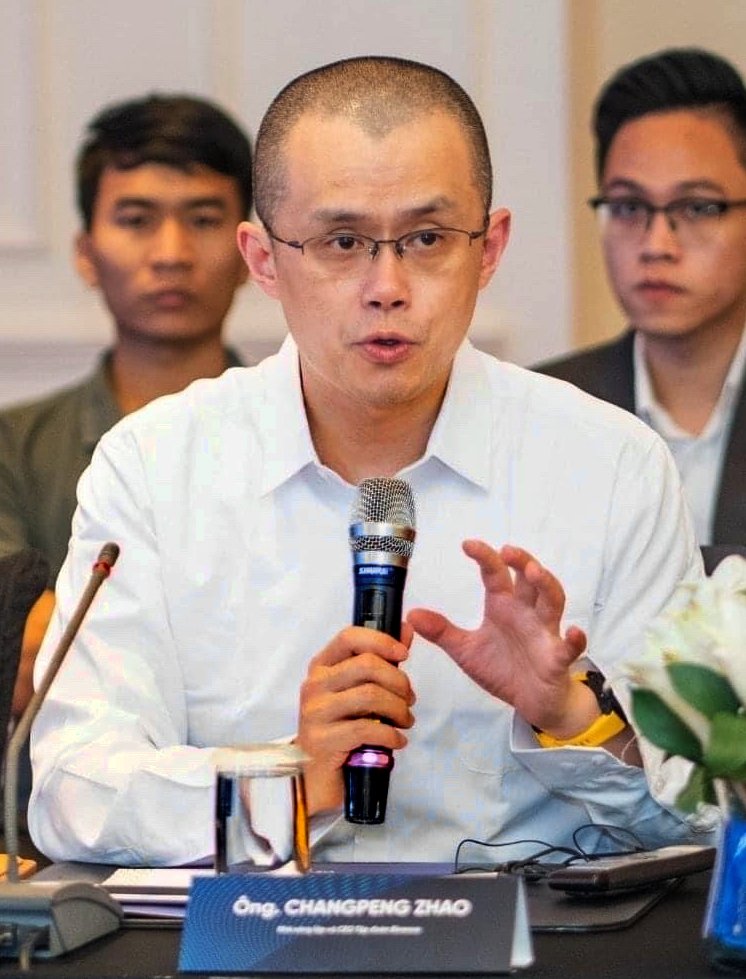
Attackers exploited a previously undetected firmware flaw in Coldcard hardware wallets, enabling thefts of more than $70 million in bitcoin, prompting Binance founder Changpeng Zhao (CZ) to urge holders to diversify funds and reconsider self-custody strategies.
What Happened
On July 30, bitcoin users reported an unprecedented wave of thefts from Coldcard hardware wallets—a device widely seen as a benchmark for secure self-custody. Initial investigations revealed that a firmware bug, present since March 2021, had fatally weakened the random number generation process used to create wallet recovery seeds on impacted Coldcard models. This flaw allowed attackers to reconstruct the private keys for affected wallets remotely and siphon funds without ever gaining physical access to the devices. Coinkite, makers of Coldcard, confirmed the vulnerability and has since issued emergency firmware updates, urging users who generated seeds on the affected firmware to create new seeds on updated devices and migrate their assets urgently. The response from the hardware wallet provider, though prompt, could not prevent significant losses, as many compromised wallets had remained dormant for years before being targeted.
Galaxy Research analysis found that approximately 1,082.65 BTC, then valued at nearly $70 million, were drained from 1,196 addresses in about 41 minutes. The scale and speed of the attack—coupled with the fact that key material could be reconstructed without possession of the hardware—shocked security professionals and crypto holders alike. While hardware wallets remain a cornerstone for mitigating custodial risks, this incident shows that well-established solutions can still harbor deeply embedded bugs that avoid detection for extended periods. Binance founder CZ’s public comment on X, urging users to split funds across multiple wallets but noting its own risks, further highlights the gravity of the episode.
Why It Matters
The attack on Coldcard hardware wallets has reignited an industry-wide debate over the limits and complexity of self-custody. While hardware wallets have traditionally offered strong protection against centralized risk and online attacks, this incident demonstrates that even leading devices can contain flaws that remain hidden for years, potentially exposing large sums to coordinated thefts. Further, the fact that affected wallets were dormant illustrates the persistence of latent vulnerabilities in long-term, offline storage strategies.
On a second-order level, the episode exposes the practical challenges that emerge as more market participants embrace self-sovereignty. Recommendations like CZ’s—to split funds among several wallets—require end users to master advanced security procedures and key management, increasing the chance for operational mistakes. Moreover, the need for robust, ongoing independent code audits in wallet firmware becomes ever more acute as asset values and attack incentives grow. Professional investors and institutions must now reassess not just which wallet brands to trust, but how diversification, firmware provenance, and incident response factor into resilient custody approaches.
Key Takeaways
- A firmware bug in Coldcard wallets enabled remote BTC theft by reconstructing private keys from weak seeds.
- Over $70 million was stolen from nearly 1,200 dormant addresses in minutes, per Galaxy Research.
- Coinkite urges regeneration and migration of seeds; simple firmware updates do not fix compromised wallets.
- CZ advises risk spreading across wallets, despite added complexity in self-custody management.
What’s Next
The immediate focus is on rapid adoption of Coinkite’s firmware fixes and migration of funds from potentially compromised wallets. The industry will likely see renewed scrutiny of hardware wallet security models, with increased calls for independent auditing and transparency in firmware development. Analysts expect ongoing debate over whether users—or even institutions—can realistically mitigate key management risks at scale. For now, the market will be watching for additional disclosures from wallet makers, changes in user behavior, and any further emerging threats that this episode may have exposed elsewhere in the self-custody landscape.
🧠 HafidWatch Take
A critical firmware flaw in Coldcard hardware wallets allowed an attacker to drain over 1,000 BTC without physical device access. Binance founder Changpeng Zhao (CZ) urged users to diversify funds, reigniting debate about hardware wallet reliability and the complexities of self-custody risk management.
🔗 Tools mentioned in this article
Affiliate disclosure: Links above may earn HafidWatch a commission at no cost to you.
Daily crypto intelligence. Before the market opens.
Including the Divergence Index — the sentiment gap no other newsletter tracks. Free, every morning at 7:30am ET.
✓ Free forever · ✓ No spam · ✓ 50+ sources monitored